Need A Penetration Test for Compliance?
Get a Certified Pentest Aligned to Your Audit
Requirements—Done Right the First Time
Built for companies preparing for SOC 2, ISO 27001, HIPAA,
or CMMC. Without the confusion, delays, or guesswork.
"Audit passed. No setbacks.”
— Ken Weeks, Newforma
“Security approved. Deal secured.”
— Regina Foti, Protos Security
“Critical gaps identified and resolved.”
— John Gojuk, 3 Story Software
If You’re Here, You’re Likely Preparing for Compliance:
- Working toward SOC 2, ISO 27001, HIPAA, or CMMC
- You’re unsure what type of pentest is actually required
- You want to avoid delays, rework, or failing your audit
Compliance-Focused Penetration Testing—Properly Scoped and Executed
We deliver penetration testing aligned to your specific framework so you can:
- Meet audit and certification requirements with confidence
- Avoid gaps that lead to failed audits or delays
- Ensure your testing meets auditor expectations
- Move through compliance without unnecessary friction
Get It Right the First Time
- Clear scoping based on your compliance framework
- Guidance on what’s required (and what’s not)
- Efficient onboarding and scheduling
- Detailed reporting aligned to audit needs
Meet Our Team
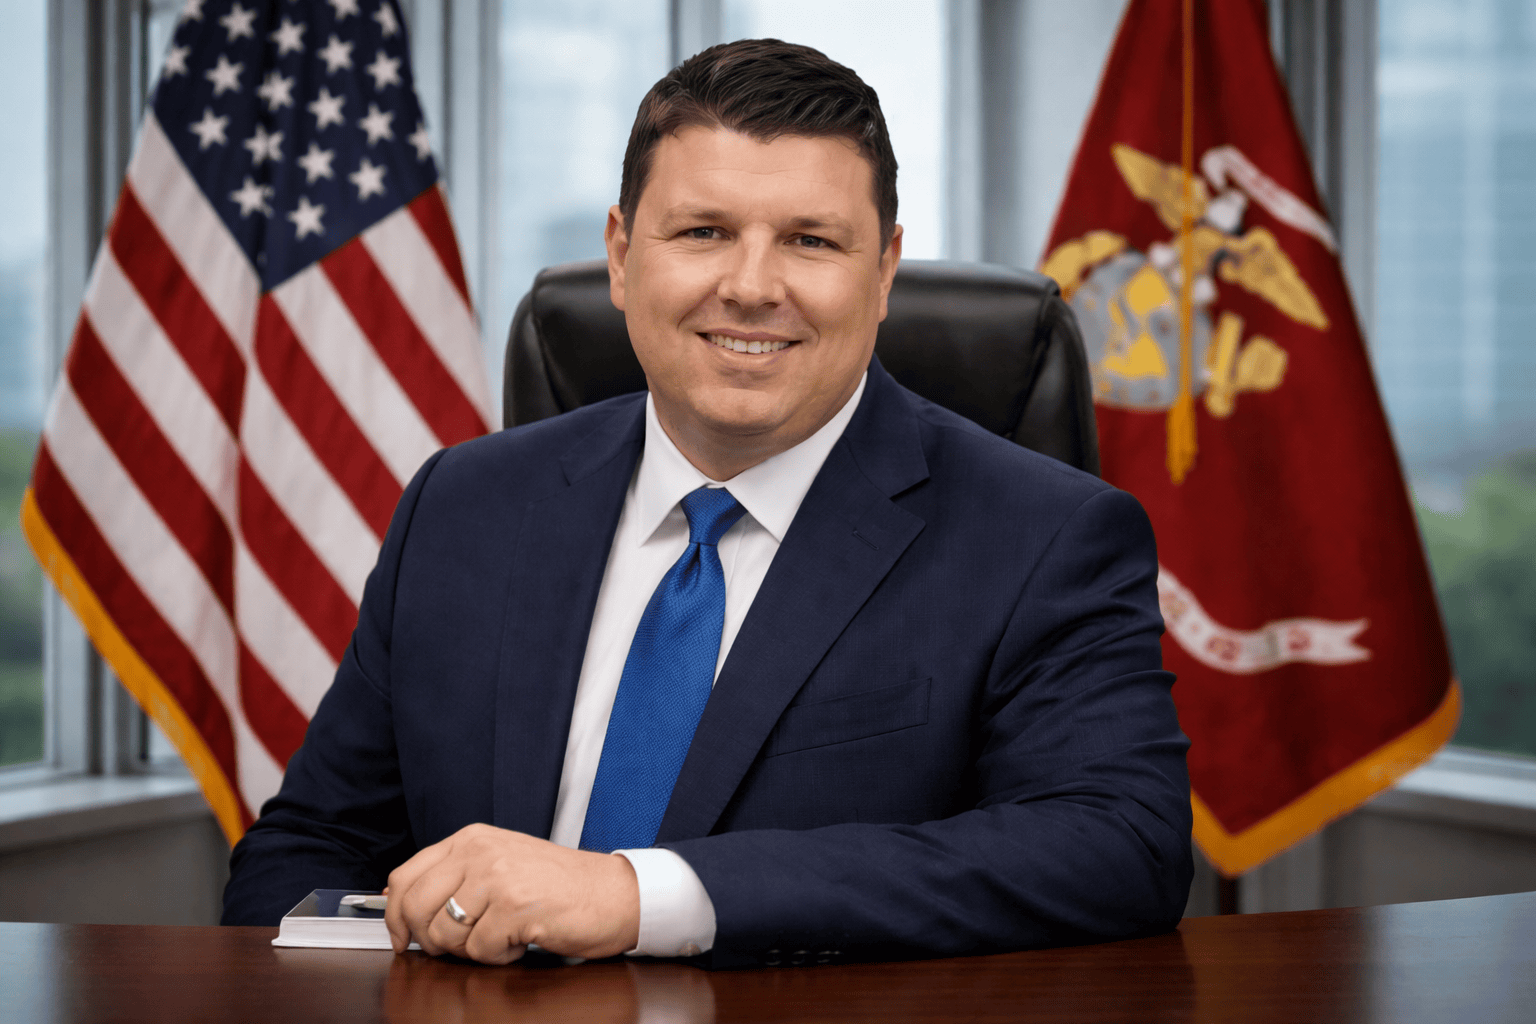
Francis Schmuff | Executive Sponsor
Renee Jones, Ph.D. | Program Manager
Bryan Siegel | Director of Compliance
CDA’s Penetration Testing division is led by seasoned military operators who bring battlefield-proven discipline and cybersecurity expertise into the civilian sector, delivering rigorous, real-world defense for modern organizations.